

The stages of a run
Each run has five stages.1
Map the attack surface
The agent reads your knowledge graph to find all applications and HTTP endpoints in your authorized domains. The agent also reads the source code of your connected repositories. The source code shows routes that are not in the graph yet, such as routes added after the last scan. The agent reads the graph at the start of each run. Thus, each run includes new surface.
2
Examine each vulnerability class
Each vulnerability class has a specialist agent. Each specialist examines the full attack map with the source code and the live application. The specialist records each candidate issue that it finds.
3
Exploit each candidate again
A different agent, the verifier, exploits each candidate again on the live target. A candidate becomes a finding only if the verifier triggers it and the result has an impact. A stability check then reproduces each finding again. The check removes findings that do not reproduce each time.
4
Score, explain, and chain
Each finding gets a CVSS v4.0 score and a root cause. The root cause points to the code. Some low-severity findings share an asset. The agent can combine these findings into one attack chain with a higher severity.
5
Report and check coverage
The agent writes the report and compares it with the graph. The report lists the endpoints that no test touched. These endpoints are coverage gaps.
Vulnerability classes
By default, each run tests these vulnerability classes:Tests with and without a login
Without credentials, the agent tests what an anonymous visitor can reach. With test accounts, the agent signs in and tests what a signed-in user can do. Give the agent two accounts with different roles. Then it can test for privilege escalation and for data that leaks between users.Limits
The agent tests only the hostnames in your authorized domains. The agent sends state-changing requests (PUT, PATCH, DELETE) only when Allow state-changing requests is on. This setting is on by default. See Safety and authorization.
The agent does not change your code or your infrastructure. The agent gives you the fix, and you decide what to ship.
Run statuses
You can see the status of each run in the app and in Mission Control.
A completed run: the run, the number of paths that it tested, its duration, and its target.
Runs with no findings
A completed run with no findings means this: the agent did not reproduce an issue on the surface that it tested. Mission Control shows this run with its result. Thus, you can see the difference between a run with no findings and a run that did not start.Run results
Each run shows three counts. The counts show the same issues at three levels of certainty.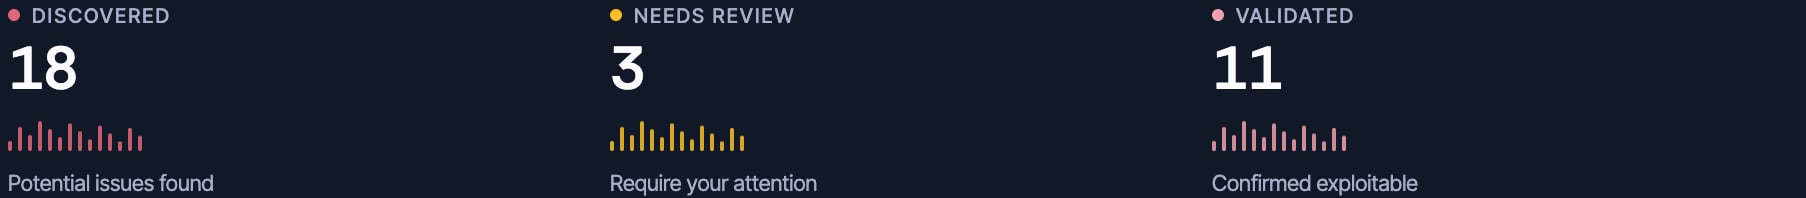
Discovered, Needs review, Validated.
For the parts of a single finding, see Understand a finding.
Next steps
Define scope
Enable offensive testing on domains and add test accounts.
Keep up with production changes
Set the schedule to match your releases.